One of the main goals of the new Data Protection Regulation is to make the enforcement of data protection legislation more efficient. This can be seen in the fact that national supervisory authorities have been granted the power to impose very large fines for unlawful data processing.
20.3.2017
Get a Handle on Data Protection Risks and Seize New Business Opportunities
Tags
Almost all companies process personal data, which makes them data controllers obligated to comply with data protection legislation. In this respect, the new regulation makes data protection a part of corporate risk management on an entirely new scale. In order to ensure that they identify, manage and minimise these risks properly and efficiently, companies must look beyond their own business risks and keep in mind whose risks they are really dealing with.
Data Protection Risks Are Individual Risks
The purpose of personal data legislation is to protect the rights of individuals—you, me, everyone—to data privacy. The risk that personal data will be abused also primarily affects individuals. If you look at the numbers, the legislator has really spelled this out in the new regulation: the word ‘risk’ appears in the new regulation about 70 times—a ten-fold increase over the current Data Protection Directive.
The Data Protection Regulation emphasises the data controller’s duty to plan its data processing procedures in such a way that the risks on the level of individuals are taken into account proactively. This requires more of companies than just incorporating data protection risks into their existing risk management processes—risk awareness needs to be present in data protection work that data controllers engage in on every level.
Without making an assessment of the potential effects on individuals, the effective implementation of data protection legislation is impossible. How can companies choose the correct legal grounds (such as determining whether the data controller’s legitimate interests are in balance with the rights of individuals) or determine the proper level of data security without knowing what the risks to the individual are?
Be Systematic
According to the principle of privacy by default, companies need to identify and account for risks to individuals well before starting to process data. Companies should adopt some kind of privacy impact assessment to systematically assess and document the risks relating to data processing.
One of the major changes being brought by the new Data Protection Regulation is accountability. It is no longer enough that a company’s actions are compliant, they have to be able to demonstrate it. The risk management methods mentioned above are a key part of fulfilling this obligation.
Systematic data protection procedures that take the risks to individuals into account will not only shield companies from fines and other penalties, but maintain the public’s trust in the company. This trust then forms the foundation for the next step, in which data protection ceases to be a risk and becomes a business opportunity. This should be the long-term goal of every company.
Latest insights
Article published 26.10.2026 – FDI Regulatory Service
Reform of Finnish FDI screening moves forward: significant changes and broader scope
 Article published 1.10.2026 – Financial Regulation
New EU-driven banking M&A rules entered into force in Finland on 1 October 2026
 Article published 24.9.2026 – Environment, Energy & Green Transition
Electricity Market Act: Proposed priority procedure to significantly change new electricity network connections in situations of scarce capacity

 Article published 11.9.2026
Finland proposes a new data centre register – draft legislation open for comments
Kiti Karvinen, Joachim Wik & Johanna Kyllöinen
Hannu Huotilainen
Marius af Schultén, Kanerva Sunila, Samuli Tarkiainen, Jonas Holm & Noora Ahonen
Marius af Schultén, Antti Kaakkola, Samuli Tarkiainen, Mikko Alakare, Janne Juusela & Jerker Pitkänen
Latest references
Cibus Real Estate – Acquisition of three retail properties
We advised Cibus Real Estate AB (publ) on its acquisition of three newly built retail properties in Pori, Finland. Kesko is the tenant in all three properties, and the average lease term is 8.1 years. Cibus is a real estate company listed on Nasdaq Stockholm Mid Cap. The company’s business concept is to acquire, develop and manage properties in Europe with daily goods chains as anchor tenants. The company currently owns approximately 700 properties in Europe.
Case published 12.11.2026
Seaya Nova and Molten Ventures – USD 80 million series C financing of Pliant
We advised Seaya Nova and Molten Ventures as Finnish counsel in connection with the USD 80 million Series C financing of Pliant, a Berlin-based fintech specialising in B2B payment solutions and corporate credit cards. The financing round was led by Seaya Nova and Speedinvest, with participation from Illuminate Financial, Motive Partners, Molten Ventures and Citi Ventures. Founded in Berlin in 2020, Pliant provides modular payment solutions for businesses and holds an EU e-money licence in Finland as well as a licence from the UK Financial Conduct Authority. We advised on the Finnish law aspects of the transaction alongside YPOG, which acted as lead counsel to Seaya Nova and Molten Ventures.
Case published 12.11.2026
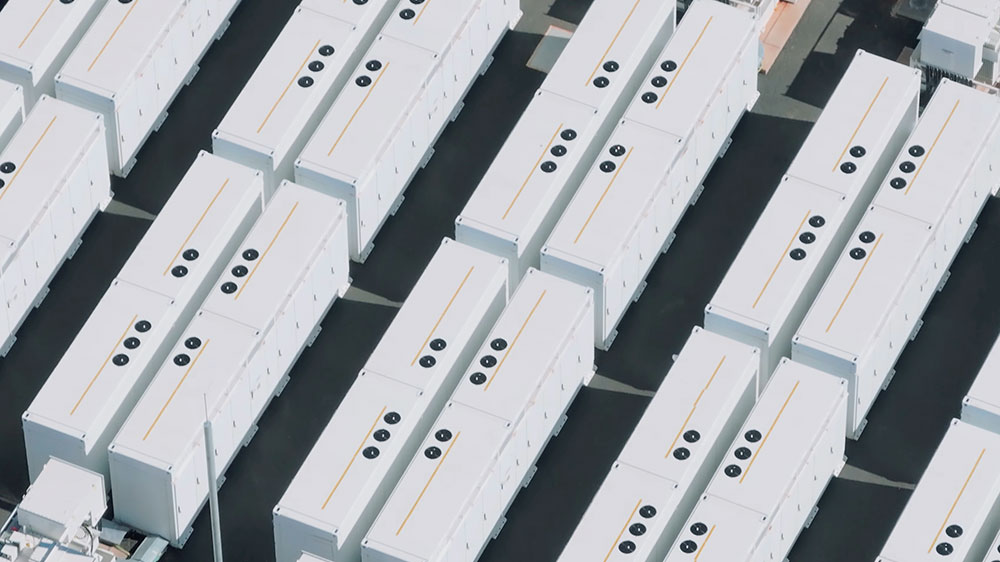
Nala Renewables – Development, acquisition and financing of battery energy storage system (BESS) project
We advised Nala Renewables on the Finnish law aspects of the development, acquisition and financing of its battery energy storage system (BESS) project in Vuolijoki, Finland. The project comprises a 125 MW / 250 MWh battery energy storage system. Our advice extended beyond financing to the transaction’s legal due diligence and the acquisition of the project company. We also advised on key project contracts and financing documentation for the project finance facilities provided by Coöperatieve Rabobank U.A. The project is part of Nala Renewables’ growing portfolio of battery storage assets in Finland and the wider Nordic region, supporting the integration of renewable energy and contributing to the flexibility and stability of the Finnish electricity grid.
Case published 3.11.2026
Foundation Clinic – Funding Round
We advised Foundation Clinic in connection with its funding round backed by a group of prominent Finnish technology entrepreneurs and investors, including founders behind Supercell and Wolt. Foundation Clinic is a Finnish healthcare company developing a new approach to private healthcare focused on preventive, data-driven and continuous care. The company aims to combine comprehensive health data with ongoing medical care to identify and address health risks at an early stage.
Case published 29.10.2026