Privacy professionals received a real Christmas present on 17 December when the LIBE committee voted on and confirmed the content of the new General Data Protection Regulation (GDPR). The regulation will be formally adopted early next year and will thus enter into force after a two-year transition period in 2018.
17.12.2015
Finally Agreed – New EU Data Protection Regulation Is Here!
Eija Warma-Lehtinen
The GDPR sets forth several new obligations for data controllers and processors, e.g. companies who process personal data in their businesses, and enforces them with substantial administrative sanctions up to EUR 20 million. This requires the companies to adjust their activities to the new requirements in the next two years. Since many of the obligations may require establishing new internal processes and positions in the company, we recommend starting the preparations immediately.
Some insights from the regulation’s main obligations:
Applicability of the GDPR: The GDPR applies to all processing of personal data, meaning any operation performed upon identifiable information of an individual (data subject) within the EU. In addition, the GDPR applies to the offering of goods and services in the EU and to the monitoring of data subjects’ behavior within the Union, regardless of the location of the company.
Consent for processing: When the processing is based on the consent of the data subject, the consent must be freely given, specific, informed and unambiguous. A clear affirmative action of the data subject, such as ticking a box themselves, is required. Explicit consent is required for processing special categories, e.g. sensitive data such as political or religious opinions or genetic data.
Children in social media: The processing of personal data of children in information society services requires consent from their parents. The GDPR leaves it up to EU member states to decide at which age between 13 and 16 children are capable to give consent themselves.
Rights of the data subject: Companies have to inform data subjects in clear and plain language about the processing of their personal data. In addition, the data subject is entitled to access data concerning him or her as well as have inaccurate data deleted or completed. Furthermore, data subjects can object to the processing of their personal data, which requires the controller to cease processing if the controller has no compelling legitimate interest to continue processing.
Right to be forgotten: The data subject can have his or her personal data erased if the data is no longer necessary or if legal grounds for processing no longer exist.
Data portability: Data subjects have the right to receive their personal data in a structured and commonly used machine-readable format so that they may transfer the data between service providers.
Profiling: The regulation defines profiling as processing of personal data consisting of using the data to evaluate, analyse or predict the behaviour or other aspects of an individual. Data subjects have the right to not be subject to profiling based on purely automated means when that produces legal effects on them, for example, refusing a credit application online.
Data processors: A written contract specifying the duties of both parties is required between the data controller and processor. Controllers are, thus, advised to review their existing agreements in order to verify their compliance with the GDPR.
Data breach notification: Data controllers have to notify the supervisory authority of data breaches no later than 72 hours after becoming aware of an incident, if the breach likely poses a risk to the rights and freedoms of individuals. A data processor has the obligation to notify the controller on behalf of which it is processing personal data. The controller also has to inform data subjects if it is likely that the breach results in a high risk to their rights and freedoms.
Data protection impact assessment: An assessment of the risks of data processing poses to individuals’ rights and freedoms is required when the processing consists of profiling, concerns sensitive data or includes large-scale monitoring of publicly accessible areas. In addition, national Data Protection Authorities (DPAs) may list other processing operations requiring an assessment.
Data Protection Officer (DPO): The controllers and processors are obliged to designate a DPO if the core activities of the company consist of processing that, by nature, scope or purpose, requires regular and systematic monitoring of data subjects on a large scale or processing of sensitive data and data related to criminal convictions on a large scale. Public authorities are required to appoint a DPO. The DPO needs to have expert knowledge of data protection law and practices and he/she can be either a staff member of the company or the task can be outsourced to a service provider. However, the DPO may fulfil other duties in addition to the position. The DPO’s tasks include monitoring the compliance with the regulation and to fulfill its obligations in the activities of the company.
Transfers of personal data: Transfers of personal data from the EU to third countries can only take place when the destination country is defined as having an adequate level of data protection by the European Commission, if appropriate safeguards such as Binding Corporate Rules or Standard Data Protection Clauses are applied or if specific derogations, such as the data subject’s explicit consent, exist. The grounds for transfers were not changed compared to the current legislation
One-stop-shop: While multinational data controllers are currently obliged to consult national Data Protection Authorities (DPA) in every country it does business, the GDPR launches a one-stop shop system where the DPA of the country where the controller’s main establishment in the EU is located acts as the lead supervisory authority. The lead supervisory authority coordinates the proceedings. However, the supervisory authorities will communicate in cross-border cases, and they may enforce decisions made by the lead supervisory authority. In addition, data subjects are entitled to lodge complaints on data processing in their own member state irrespective of the country where the company is established.
Administrative sanctions: The regulation empowers data protection authorities to impose administrative fines on companies for non-compliance with the regulation. The sanctions come in two categories. A fine up to a maximum of EUR 10 million or 2% of the total worldwide annual turnover of the company, whichever is higher, can be imposed for smaller infringements of the obligations of the controller and processor, for example, not appointing a DPO or not carrying out a data protection impact assessment. A higher fine up to a maximum of EUR 20 million or 4% of the turnover is possible in more serious cases such as infringements of the basic principles of processing, data subjects’ rights or international transfer rules.
The text of the regulation as agreed in the trialogue is available at: http://static.ow.ly/docs/Regulation_consolidated_text_EN_47uW.pdf
We strongly advise you to start reviewing the existing data processing activities in order to be prepared for the new requirements in time. Our data protection and privacy experts have conducted privacy compliance audits over the years for several major Finnish companies in different industries. We have redeveloped our privacy toolkit to assist our clients with the new requirements of the GDPR.
We will have Data Protection breakfast seminars on 14 January 2016 and 16 February 2016 (a separate invitation will follow) where we will discuss the content of the GDPR in more detail.
If you have any questions or concerns, please let us know. We wish you happy holidays!
Latest news
Latest references
Jolt Capital and Tesi – Investment in VEV
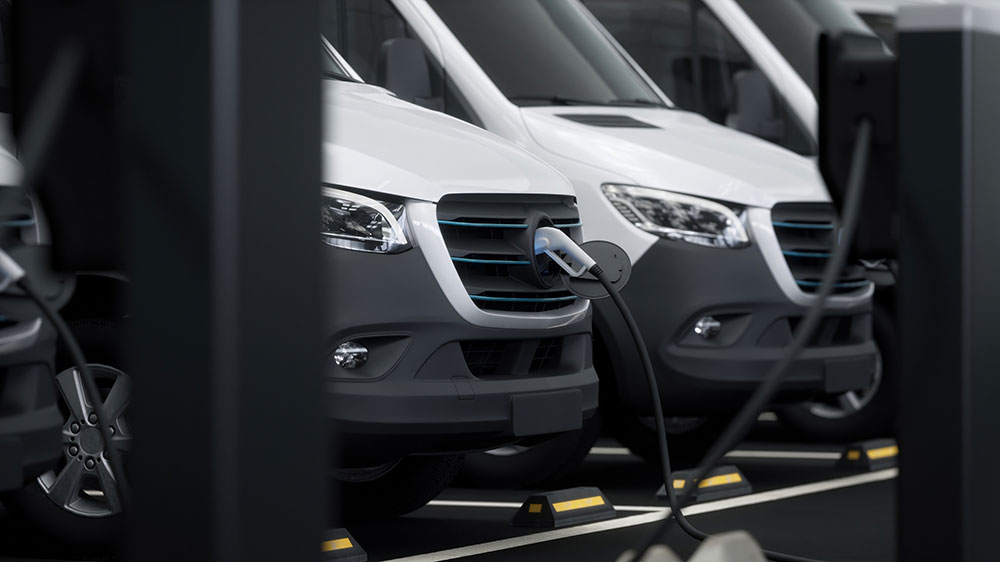
We advised Jolt Capital and Tesi in connection with their investment in VEV, a leading provider of commercial fleet electrification solutions. The investment, led by Jolt Capital with Tesi as co-investor, will support VEV’s next phase of growth and expansion across Europe. As part of the transaction, VEV became an independent company following the acquisition of Vitol’s stake in the business. Founded by Vitol, VEV provides integrated fleet electrification solutions combining fleet strategy, charging infrastructure, energy supply and operational services. Through its VEV IQ platform, the company supports more than 6,000 commercial electric vehicles across Europe and has been deployed across more than 600 sites spanning the transport, logistics and waste sectors. Jolt Capital is a private equity firm focused on growth investments in European deeptech companies. Tesi is a Finnish state-owned investment company that promotes Finnish business and economic growth through investments. We advised Jolt Capital and Tesi on the equity financing and structuring aspects of the transaction. International law firm Goodwin advised the investors on the acquisition of VEV.
Case published 10.9.2026
VR Group – Intellectual property matters
VR-Group Plc is a transport and logistics group owned by the Finnish State, operating passenger and freight rail transport in Finland with activities also in the Swedish market. VR Group provides passenger, logistics and maintenance services with over 160 years’ experience in developing responsible transport of the future. We advise VR Group in intellectual property matters as part of the company’s wider brand protection efforts. Our assignments have included advice on copyright, design rights and trademarks, focusing on the protection of the company’s visual identity – including its distinctive green colour – in connection with transport services as part of a comprehensive IP protection strategy. VR Group’s consistent brand building has also received recognition, including the Finland Chamber of Commerce’s Brand of the Year award in 2026. In the competition, brands were viewed comprehensively from various perspectives, including their story, strategic role, brand renewal ability and intellectual property protection. The jury found that VR had understood the importance of the protection of its brand as part of a comprehensive business strategy.
Case published 9.9.2026
NoHo Partners – EUR 50 million secured notes and EUR 97 million senior secured facilities agreement
We advised NoHo Partners Plc on the issuance of EUR 50 million senior secured floating rate notes. The notes have a tenor of four years and mature on 10 September 2030. The notes bear interest at a rate of three-month EURIBOR plus a margin of 4.375 per cent. per annum. The notes were allocated to a mix of domestic and international investors. We also advised NoHo Partners on the negotiation of its new senior facilities agreement. The facilities agreement comprises a EUR 60,000,000 term loan facility, a EUR 10,000,000 capex facility and a EUR 27,000,000 revolving credit facility. “We are delighted by the interest investors have shown in the company’s Notes, which reflects confidence in our strategy. The successful issuance of the Notes, together with the new loan agreement, extends the maturity profile of our financing and enables the company to continue executing its growth strategy going forward. I would like to thank all investors for their participation, as well as our partner bank for the excellent execution of the Notes issuance”, says Jarno Suominen, CEO of NoHo Partners. OP Corporate Bank plc acted as the sole lead manager and bookrunner for the issue of the notes. NoHo Partners Plc is a Finnish group established in 1996, and it specialises in restaurant services being the creative innovator of the Northern European restaurant market. The company was listed in Nasdaq Helsinki in 2013 becoming the first Finnish listed restaurant company, and it has continued to grow strongly throughout its history. NoHo Partners’ vision is to be the leading restaurant operator in Northern Europe.
Case published 4.9.2026
Topfoods – Acquisition of Delice Plus
We advised Topfoods Oy, a Triton-backed Geia Group company, on its acquisition of Oy Delice Plus Ab, a Finnish supplier of cakes and pastries. Through the acquisition, Topfoods strengthens its retail business and further reinforces its position in the cakes and pastries segment. Founded in 2008, Topfoods supplies selected food products to professional kitchens, the retail sector, and the food industry.
Case published 4.9.2026